Web Standards and Security Facing Paradigm Shifts as W3C Launches 2026 Survey Amid Surprising Browser Vulnerabilities

The landscape of web development is experiencing a profound period of transformation, marked by significant paradigm shifts in how browsers process information, how developers write markup, and how malicious actors exploit seemingly standard user-interface mechanics. Amid this rapid evolution, the World Wide Web Consortium (W3C) has officially opened its 2026 community-wide survey, seeking critical input from global developers, engineers, and digital stakeholders to shape the future direction of web standards and organizational operations. This development coincides with a flurry of industry revelations, ranging from newly emerging HTML capabilities to alarming security research exposing how standard styling languages can be weaponized within user inboxes.
As the web matures past its third decade, the friction between backwards compatibility and modern performance demands has never been more pronounced. Industry veterans and security specialists alike are urging a fundamental reevaluation of legacy practices, browser resource management, and the security boundaries traditionally trusted by end users.
The W3C 2026 Community Survey: Steering the Future of Open Web Standards
The launch of the W3C 2026 community-wide survey marks a crucial milestone for the organization tasked with maintaining the foundational protocols of the internet. As web applications increasingly rival native desktop and mobile software in complexity, the W3C faces mounting pressure to accelerate the ratification of standards that bridge the gap between web capabilities and system-level performance.
Historically, the W3C has navigated a delicate balance between enterprise requirements, browser vendor implementations, and open-web advocacy. In recent years, critics and developers have frequently pointed to the sluggish pace of HTML standardizations compared to the rapid iterations seen in CSS and JavaScript frameworks. Through the 2026 survey, the consortium aims to capture direct feedback on emerging needs—such as native media management, spatial computing interfaces, and enhanced privacy frameworks—to streamline its roadmap.

Industry analysts note that this year’s consultation is particularly vital due to the fragmentation caused by proprietary framework ecosystems. By gathering empirical data directly from the developer trenches, the W3C hopes to reclaim its role as the primary architect of a unified, interoperable web, ensuring that future standards reflect actual engineering pain points rather than theoretical ideals.
Modern HTML and the Quest to Eradicate Legacy Artefacts
While HTML traditionally evolves at a measured pace, developers navigating the mid-2026 landscape are encountering a wave of modern additions designed to reduce reliance on heavy JavaScript libraries. Technical educator Chris Coyier recently highlighted several progressive HTML features altering the development playbook, including native geolocation elements, innovative HTML-in-Canvas implementations, streamlined camera and microphone management via usermedia, and the much-anticipated model element designed to handle 3D content natively within the markup layer.
Concurrently, a rigorous industry push is underway to purge antiquated HTML snippets and artefacts that have lingered in codebases for decades. Security and code quality researchers, such as Declan Chidlow, have published comprehensive audits identifying legacy relics that continue to populate modern templates despite offering zero utility today. Elements and directives such as conditional comments, X-UA-Compatible meta tags, and cleartype directives are increasingly flagged by linters as technical debt. Eliminating these remnants not only cleans up codebases but also reduces the parsing overhead for modern browser rendering engines, contributing to marginal gains in page load efficiency.
Architectural Challenges: The Heavy Price of the Browser Main Thread
Performance optimization remains a central obsession for frontend engineers in 2026, largely driven by the reality that the browser’s main thread is an exceptionally expensive and finite resource. In a thorough technical breakdown complete with empirical demonstrations, developer Sunhyoup Lee illustrated the steep performance costs associated with poor task scheduling on the main thread.
When single-threaded JavaScript execution is blocked by intensive layout calculations, style recalculations, or unoptimized rendering loops, user interfaces suffer from stutter, high input latency, and poor Interaction to Next Paint (INP) metrics. Modern architectural best practices now heavily emphasize task splitting, micro-batching, intelligent prioritization, and aggressive task deferral. Furthermore, the industry is seeing a widespread migration of heavy computational workloads off the main thread entirely, leveraging Web Workers and WebAssembly to maintain silky-smooth 60-to-120 frames-per-second experiences even on constrained mobile hardware.
Complementing these architectural shifts, developers are rethinking classic UI components through purely declarative means. Alexander Inkin recently detailed modern methodologies for building high-performance custom scrollbar components. By replacing traditional, heavy JavaScript arithmetic with cutting-edge CSS features, engineers can now handle complex sizing, positioning, and visibility metrics entirely within the stylesheet. This approach significantly reduces runtime JavaScript execution and aligns with the broader industry trend of letting the browser engine do what it does best: layout and paint.
Security Vulnerabilities: CSS Weaponized Inside the Inbox
Perhaps the most alarming development shaking the web security community is the revelation that cascading style sheets—long considered a benign styling language—can be weaponized against popular webmail providers. Security researcher Gareth Heyes published groundbreaking research demonstrating how malicious actors can exploit CSS parser quirks and rendering inconsistencies within email clients to execute sophisticated attacks.
Traditionally, email providers employ strict HTML sanitization and image proxies to prevent tracking, script injection, and user enumeration. However, Heyes’ research proves that advanced CSS selectors and side-channel techniques can bypass these proxies entirely. More concerningly, the vulnerabilities allow attackers to deface webmail user interfaces, exfiltrate sensitive data, and even construct functional keyloggers entirely out of CSS rules without executing a single line of JavaScript.
This discovery has sent shockwaves through the cybersecurity sector, forcing major email service providers to urgently patch their rendering engines and rethink the trust boundaries of CSS. The incident underscores a sobering reality for web security: as CSS becomes increasingly Turing-complete and powerful in its layout capabilities, the attack surface expands commensurately, blurring the historical safety line that separated style from executable logic.
Infrastructure and Domain Shifts: The Sunset of .name
Beyond browser rendering and styling concerns, foundational internet infrastructure is also shifting. Veteran technologist Neil Fraser detailed the impending termination of third-party .name top-level domain structures, outlining the operational and identity implications for individuals and organizations who have relied on the namespace for their digital footprint over the past two decades. While domain sunsets are a natural part of the internet’s lifecycle, this transition serves as a stark reminder of the impermanence of digital real estate and the importance of owning primary infrastructure rather than relying on niche naming conventions.
Tooling, Resource Ecosystems, and Minimalist Browsers
To navigate these complex technical challenges, the developer ecosystem continues to produce innovative tooling designed to improve efficiency, accessibility, and user experience.
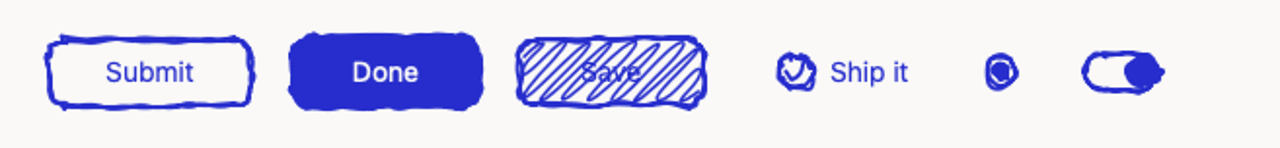
In the realm of UI resources, developer Daniel White introduced Drawably, a lightweight collection of hand-drawn UI controls. Utilizing seeded randomness for its animated pen sketches, the library boasts zero external dependencies, weighing in at approximately 7 KB of gzipped JavaScript paired with a minimalist 3 kB stylesheet. Such tools reflect a growing appetite among developers for playful, human-centric design aesthetics that do not compromise on performance.
Accessibility tooling has also seen notable advancements with the release of WCAG Radar, a localized accessibility auditing tool developed by Proper Access B.V. Offered as both a bookmarklet and a browser extension, the tool evaluates open web pages against WCAG 2.1 and 2.2 AA standards, mapping compliance results directly onto the Document Object Model (DOM) locally without transmitting sensitive page data to external servers. While advanced audits require a paid tier, the proliferation of instant, in-page accessibility testing highlights the industry’s gradual integration of inclusive design as a continuous development metric rather than an afterthought.
Finally, the desktop browser ecosystem is witnessing a minimalist renaissance. Projects such as the macOS-focused Confectionery browser are capturing the attention of power users and minimalists alike. By stripping away bloatware, heavy extension frameworks, and telemetry-heavy features, these alternative browsers aim to provide a streamlined, hyper-focused browsing experience that respects system resources and user privacy.
Implications and Outlook
As the web community processes the findings of the W3C 2026 survey alongside emerging security threats and architectural paradigms, the overarching takeaway is clear: the modern web is a double-edged sword. While new HTML elements, CSS-driven UI components, and lightweight developer tools are empowering engineers to build faster and more expressive applications than ever before, the growing complexity of browser engines introduces unprecedented security vectors and performance bottlenecks.
Navigating the remainder of the decade will require a concerted effort from standards bodies, browser vendors, and individual developers alike. Prioritizing rigorous main-thread management, closing dangerous CSS-based security loopholes, and ruthlessly eliminating legacy technical debt will be paramount in ensuring that the open web remains fast, secure, and resilient for the next generation of users.